Enterprise-grade security monitoring — without the security team.
We monitor your endpoints, keep tamper-proof logs, hunt vulnerabilities, and hand you audit-ready proof — all run for you, on infrastructure isolated to your business alone.
Every endpoint, around the clock
Your own cluster, network and firewall
Write-once, tamper-proof evidence
By default, pinnable by region
Security stopped being optional.
Four pressures now force every mid-sized company to prove its security. But a full-time SOC analyst costs €90k+/year, and 24/7 cover is out of reach. That's the gap we close.
- 01Cyber-insurance won't pay without controlsInsurers now demand demonstrable logging, endpoint detection, MFA, and vulnerability management before they'll write — or renew — a policy.
- 02Your customers audit youWinning enterprise deals means answering 200-line security questionnaires: "Do you keep tamper-proof logs?" "How fast do you detect a breach?"
- 03Ransomware is existentialOne encrypted file server can halt a business for days. Detection in minutes is the line between an incident and a closure.
- 04Leadership is personally exposedDirectors increasingly carry personal liability for negligent security. "We didn't know" is no longer a defense.
One managed service. Your whole estate, watched.
Six capabilities run continuously on infrastructure dedicated to you — so you get covered, insurable and audit-ready without building a thing.
From signed to monitored — in days, not months.
Architecture you can put in front of an auditor.
Per-tenant isolation — zero shared blast radius. Every client gets their own isolated cluster: separate VM, private network, dedicated firewall. Nothing about your security shares a wall with anyone else's.
- Configurable data residencyYour data stays in the region you require — EU/Germany by default, pinnable elsewhere for local rules.
- Immutable, write-once log storageWORM retention for 1–3 years — the tamper-proof evidence trail insurers and auditors require.
- Built on proven open-source security infrastructureBattle-tested endpoint agents, a SIEM and a standing vulnerability scanner — not an opaque black box.
- Fully automated, click-to-deploy onboardingProvisioning your isolated environment is automated end to end — fast to stand up, consistent every time.
Transparent, and a fraction of a hire.
No surprise enterprise quotes. Two simple lines, tiered by the size of your estate.
One-time
We deploy agents, wire up log ingestion across firewalls, servers and cloud, and map your estate into your own isolated cluster.
- Click-to-deploy provisioning
- Dedicated VM, network & firewall
- Estate mapped in days
Tiered by endpoint count and log volume
24/7 detection, vulnerability scanning, immutable log retention and audit-ready reporting — all run for you.
- 24/7 monitoring & alerting
- Monthly audit-ready PDFs + live dashboards
- Immutable 1–3 year log vault
An in-house junior analyst costs €60,000+ a year — and still won't give you 24/7 cover. We do, for a fraction of that.
Need EU NIS2 compliance?
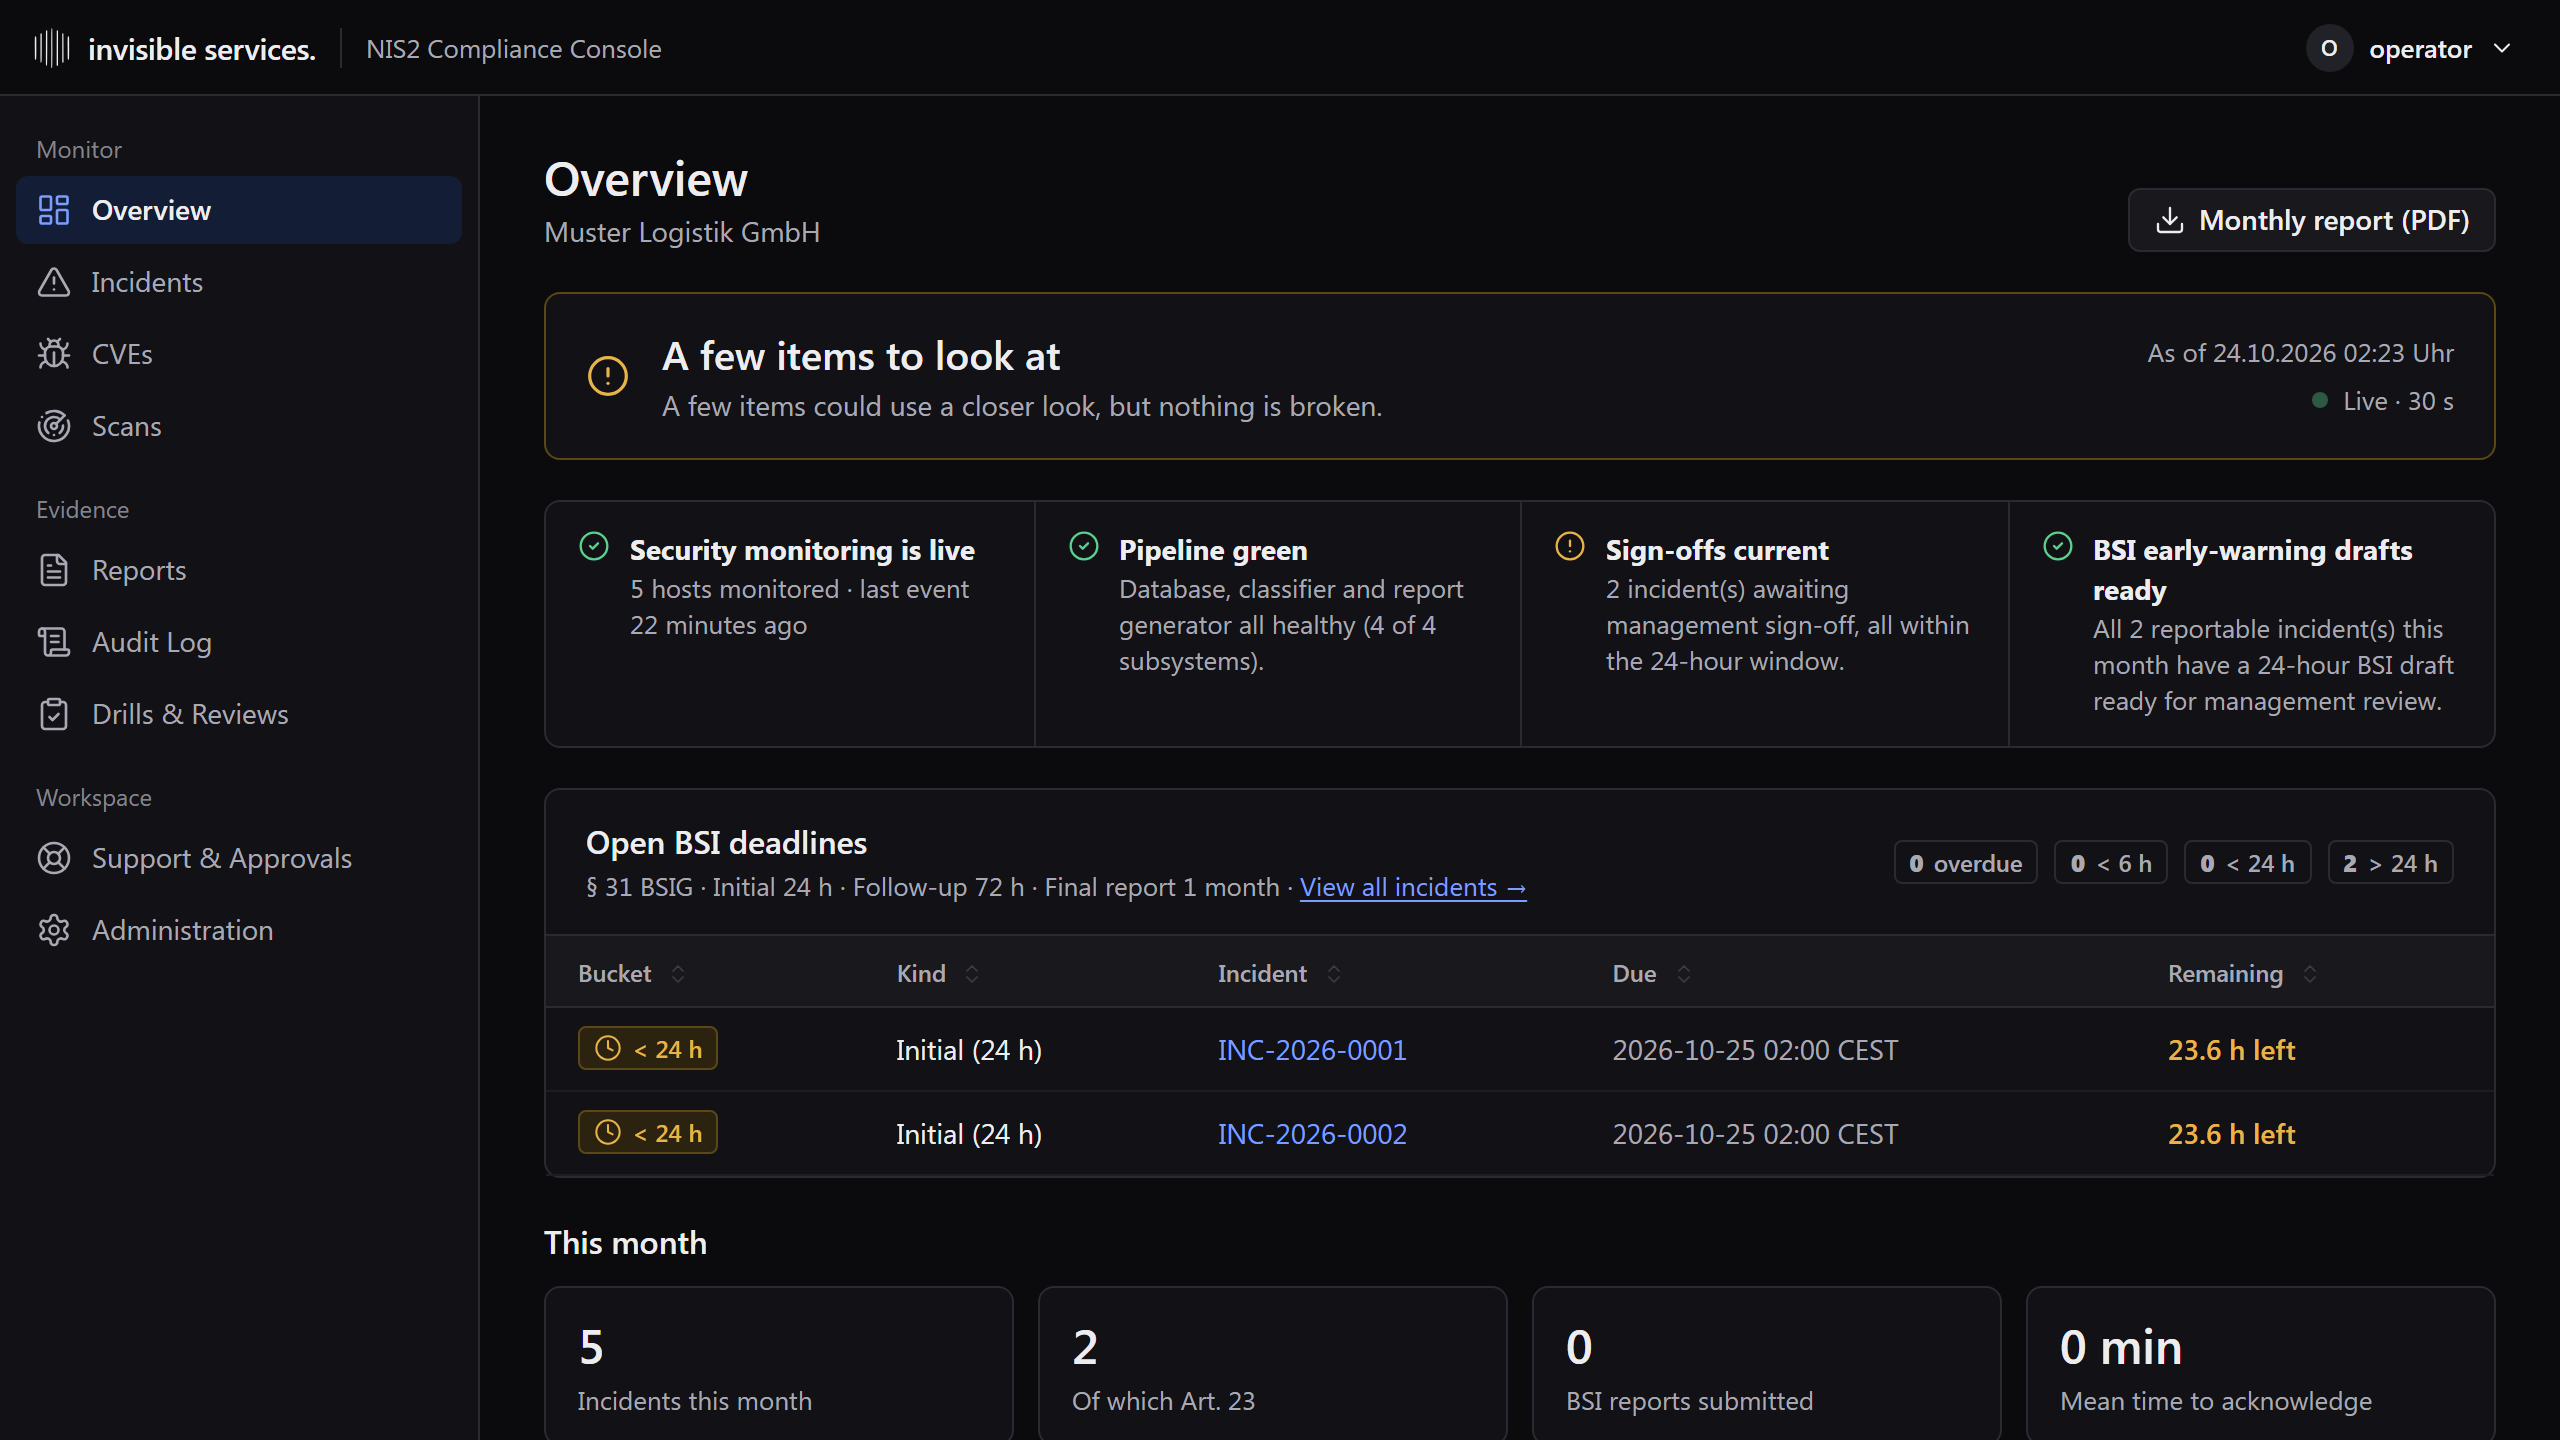
For EU and German clients, an optional module adds full NIS2 Article 21(2) coverage — plus an Article 23 pipeline that auto-drafts your regulator report within minutes. The global platform leads with monitoring and audit; this is the "and, if you're in the EU…" piece.
Read the German NIS2 pageArticle 23 — incident-report drafting
- 01We detectA reportable incident fires on your estate.
- 02We draftYour BSI report and forms are auto-drafted with the technical detail pre-filled, ready well inside the 24-hour deadline.
- 03You review, approve & submitYou approve with one click and file it with the regulator yourself. We prepare the paperwork; the submission stays in your hands, because you're the regulated entity.
Get your free Security Readiness Scan.
We scan your estate and hand back a report showing exactly where you fail basic monitoring, logging and vulnerability hygiene — the same artifact insurers and your customers will ask for.
- See where you'd fail an insurer's controls checklist
- Spot gaps in logging, endpoint coverage and patching
- No obligation — keep the report either way
Thanks — your readiness scan request is in. A specialist will reach out within one business day to confirm scope and get you a report.
- We confirm scope & access (read-only)
- We run the scan across your estate
- You get a plain-English report — yours to keep